About SECURIQUE
A fractional CISO for startups that aren’t ready for a full-time hire.
A senior security leader embedded in your team, without the $200k salary, the overhead, and the months it takes to hire. Three ways to work with us: an ongoing fractional CISO retainer, a scoped penetration test, or a fixed-price AI Governance Gap Assessment. See the services.
Why SECURIQUE exists
Every startup hears the same thing: you need a security program. But the usual options don’t fit. A full-time CISO costs $200k+ and takes months to hire, and most early teams don’t need a full-time one yet. Agencies sell you a senior name, then quietly hand the actual work to juniors. Freelancers run a one-and-done assessment and disappear. None of it gives you security that actually sticks.
SECURIQUE is the fractional model done right. One named senior owns your engagement end to end. You meet that person before you sign, and they stay accountable for every deliverable. When a piece of the work calls for a specialist, we tell you who and why up front. Nothing gets quietly passed to a B-team. Embedded in your team, on an ongoing retainer, scoped to where you actually are. We join your sprints, your architecture reviews, and your incident response, and we move at your pace.
We exist to make senior security leadership accessible to startups at every stage.
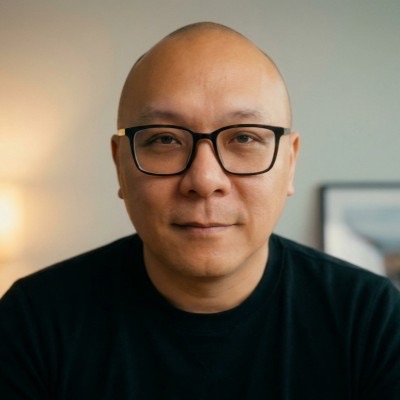
Who’s behind it
Hi, I’m Que Sengmany. I founded SECURIQUE and I lead the work.
25+ years across network engineering, cloud architecture, application security, DevSecOps, and security leadership. I’ve built and led security programs from inside cloud-first, engineering-driven companies, not from the outside looking in.
Certifications include CISSP, OSCP, and AIGP, with ISO 27001 Lead Auditor training. I’ve broken into systems and built the programs that defend them, and these days I help teams govern AI responsibly. When you hire SECURIQUE, I’m the named lead on your engagement and I stay accountable for it start to finish. Where the work calls for a specialist, I bring in someone senior I’ve worked with, name them before we start, and own the result.
Capability index
What to expect
-
You work directly with the founder, and you meet anyone else who touches the work before it starts.
-
Security is scoped to your stage. We start with whatever is blocking you, not with a rigid framework.
-
We embed in your workflow: a weekly sync, async Slack in between, and a seat in sprint planning, architecture reviews, and incident response.
Ready to build your security program?
Book a free 30-minute call. We’ll walk your stack, your timeline, and whatever is blocking the deal, then tell you honestly whether we’re a fit and which engagement is the smallest one that solves it. The gap assessment starts right there. You’ll see exactly what’s included before you commit.